

Choose the smallest scope
For a first request, selectproject:read. It is enough for GET /v1/whoami. Add only the scopes needed for the documented testnet account, mandate, action, and webhook operations. A scope does not give an API key owner authority over a mandate.
The test environment is available through the hosted public API and, for developers with access to the unpublished password gate, console.gol.network. Existing test API keys work directly with the public API. Live project and credential creation returns capability_unavailable; GOL does not currently support a live or mainnet setup.
Keep keys on the server
Send the key in theAuthorization header from a backend service:
Rotate or revoke
Rotate a key when you need to replace it without an abrupt cutover. The local console supports a bounded overlap window so your server can switch to the new secret. Update your server configuration, verify a request using the new key, then let the old key expire or revoke it. Revocation immediately makes the old key unusable.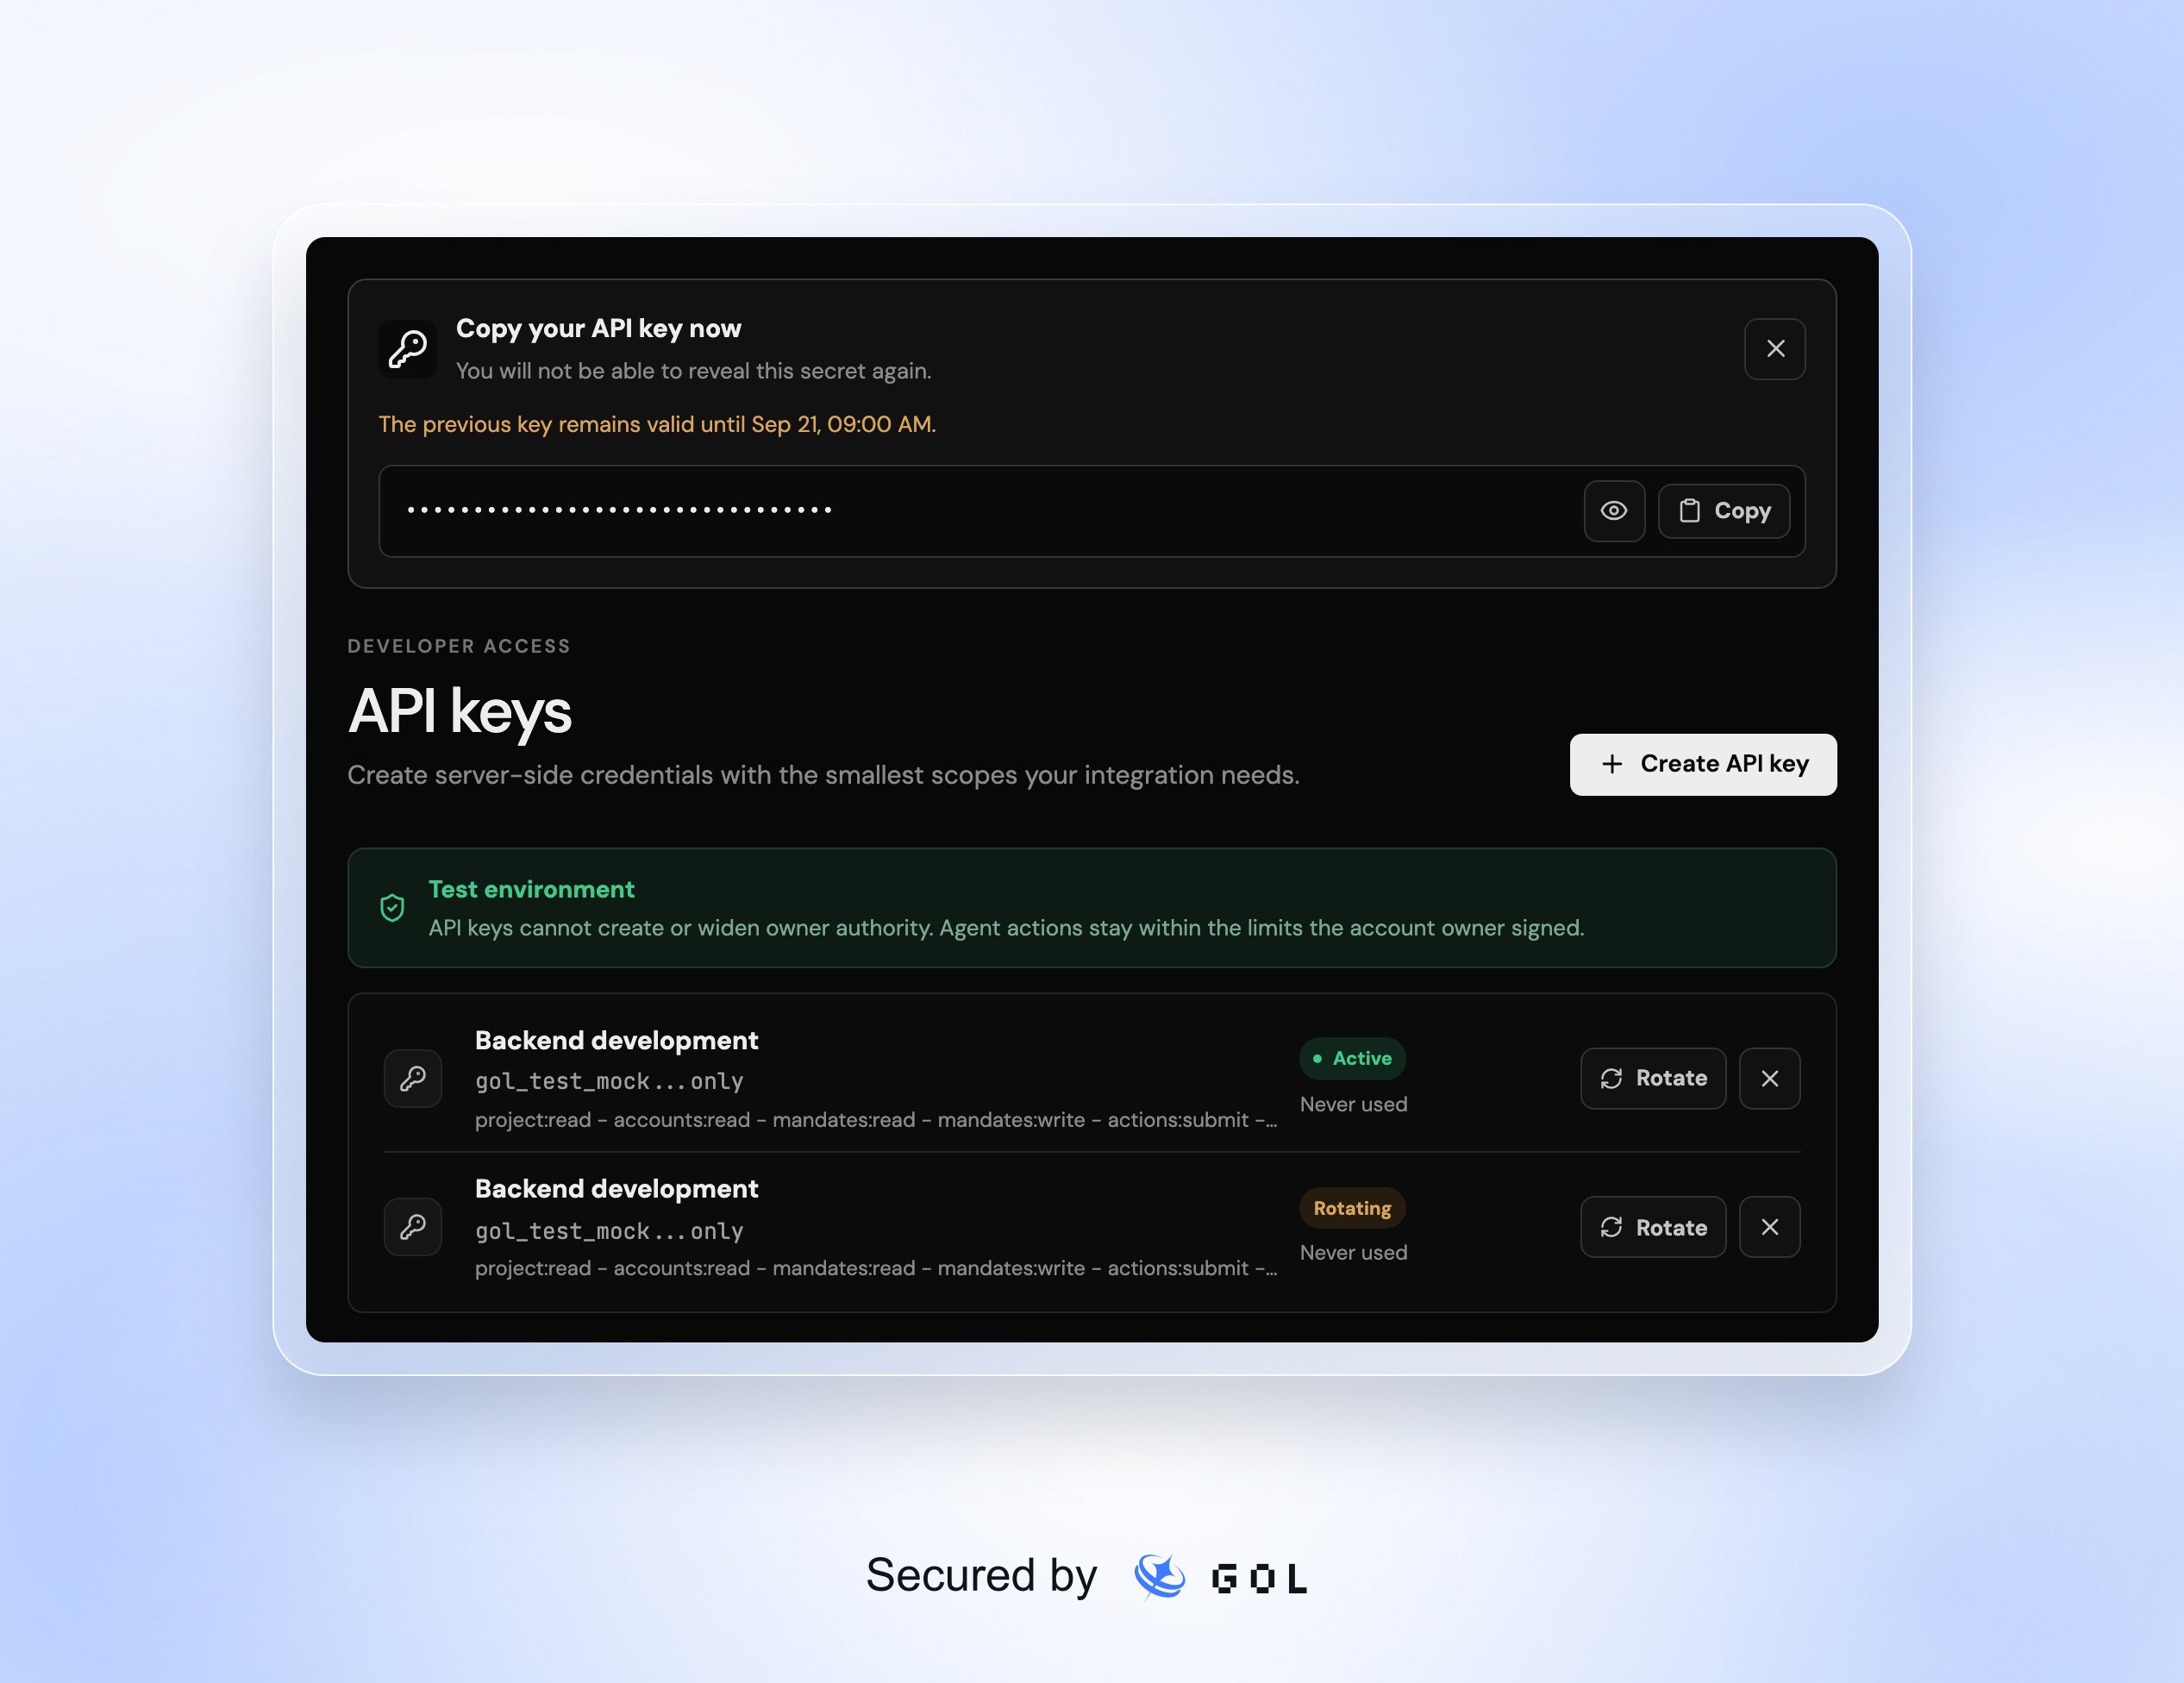
After a rotation, the new key is Active and the previous key shows Rotating until its overlap ends. The X button asks for confirmation, then revokes the key.