

approve.gol.network, in a top-level desktop popup or a full page on mobile.
The developer application cannot replace terms or signing data inside that origin.
The contracts enforce limits and direct owner approval, pause and revocation remain
possible without GOL. The page cannot force every developer to use hosted review.
Register a return destination
In Project settings, register an exact HTTPS callback without query or fragment. Publish the project-bound TXT challenge at_gol-approval.<domain> and verify it.
A project name is display metadata. A verified domain proves control of the callback
host; it does not authenticate the developer’s end user. Revocation blocks new
signatures and return navigation, and does not cancel an accepted signature.
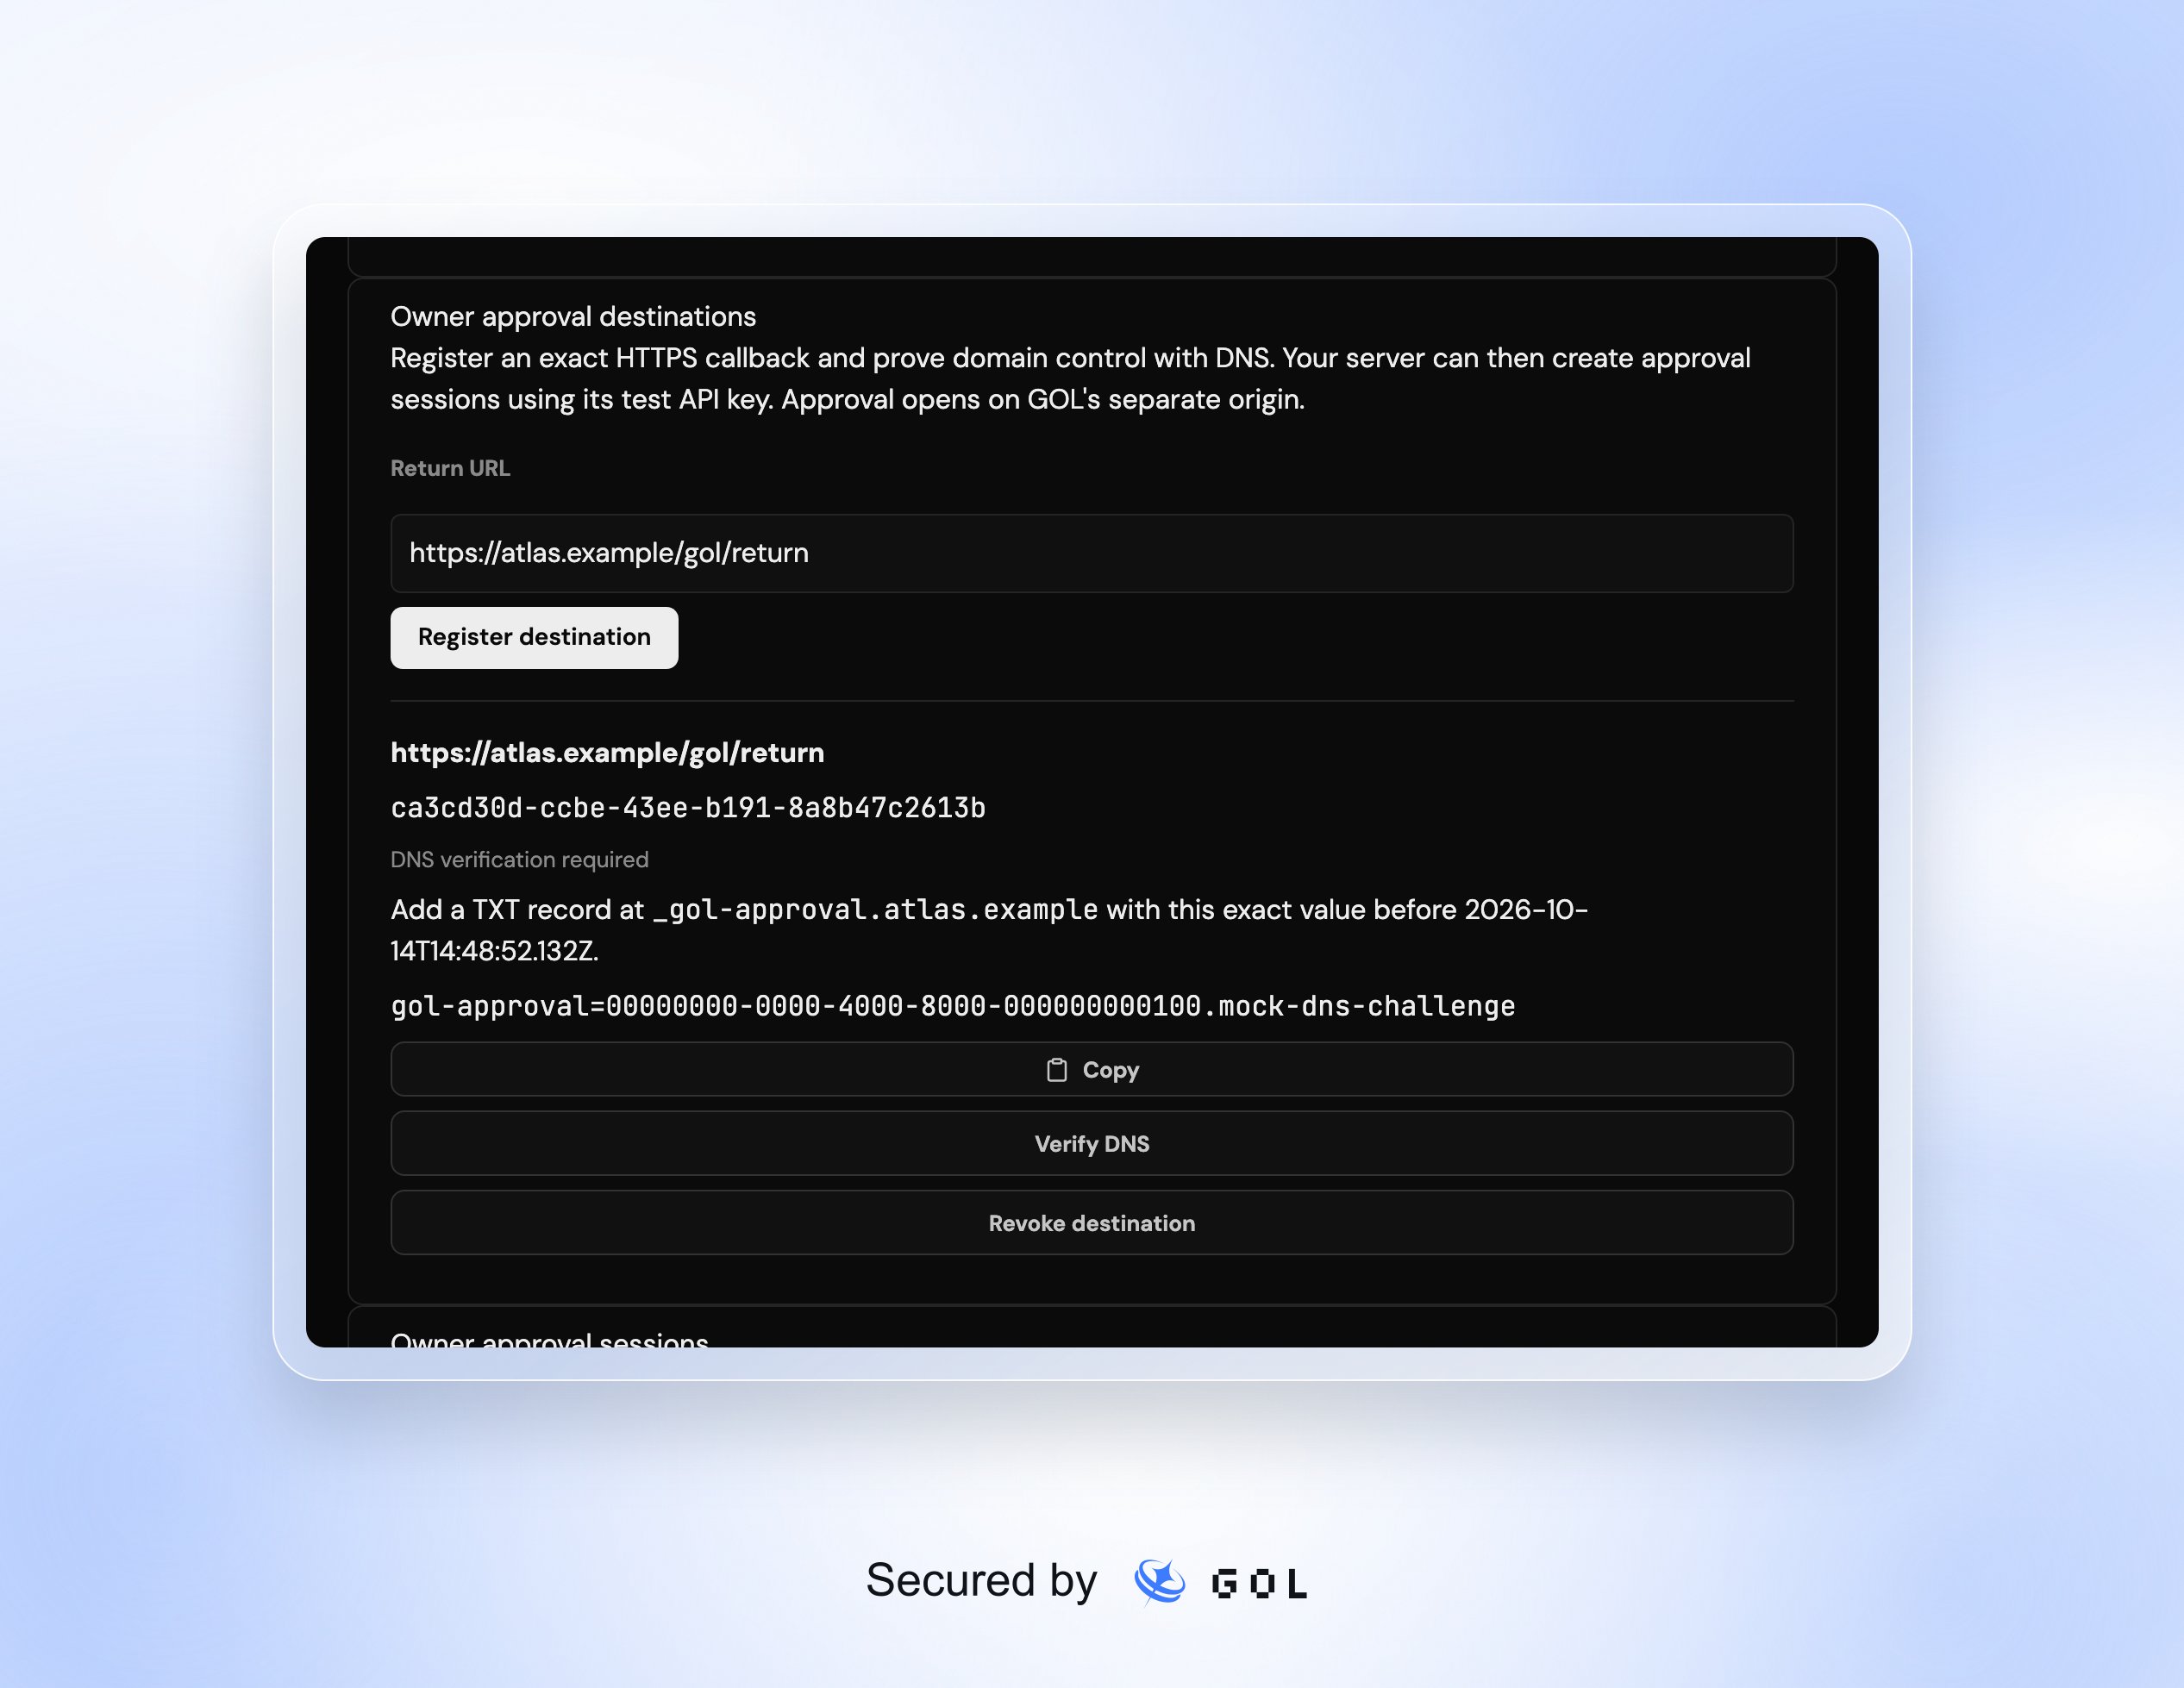
Project settings registers and verifies the exact approval return destination. This console capture uses deterministic mock data.
Prepare and create on your server
Keep the test project API key on your server. Prepare the exact mandate throughprepareGasPolicy, then create a session for the returned draft and registered
destination. Persist the returned session ID, request ID and authority fingerprint
with your application’s request before sending the launch descriptor to the browser.
Open directly from a click
Obtain the descriptor before the user clicks, so browser activation can open a popup. The browser imports the browser-safe entry only and receives no project API key.resumeOwnerApproval() once to consume the correlated result. The SDK stores
only non-secret correlation, never a capability, in session storage. Popup closure
returns closed; it does not reject, approve or revoke. If your application uses
COOP, test its opener behavior and offer the redirect path when messaging is severed.
Review, sign and verify
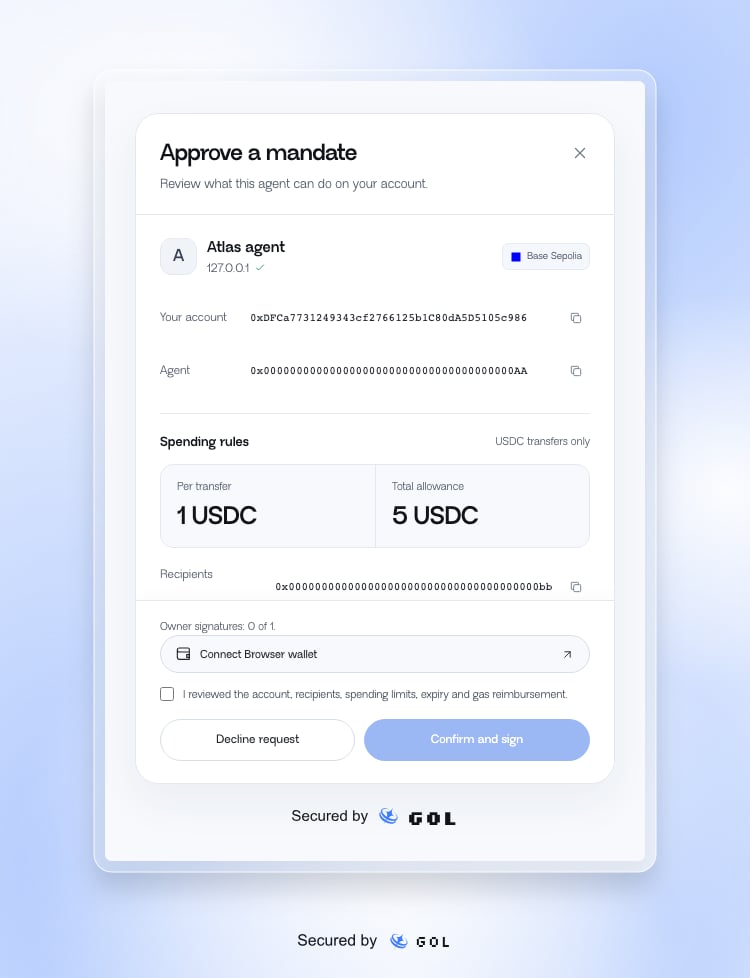
The desktop popup is 540 by 780 pixels. Canonical authority supplies the readable account, recipient, spending, expiry and gas terms.
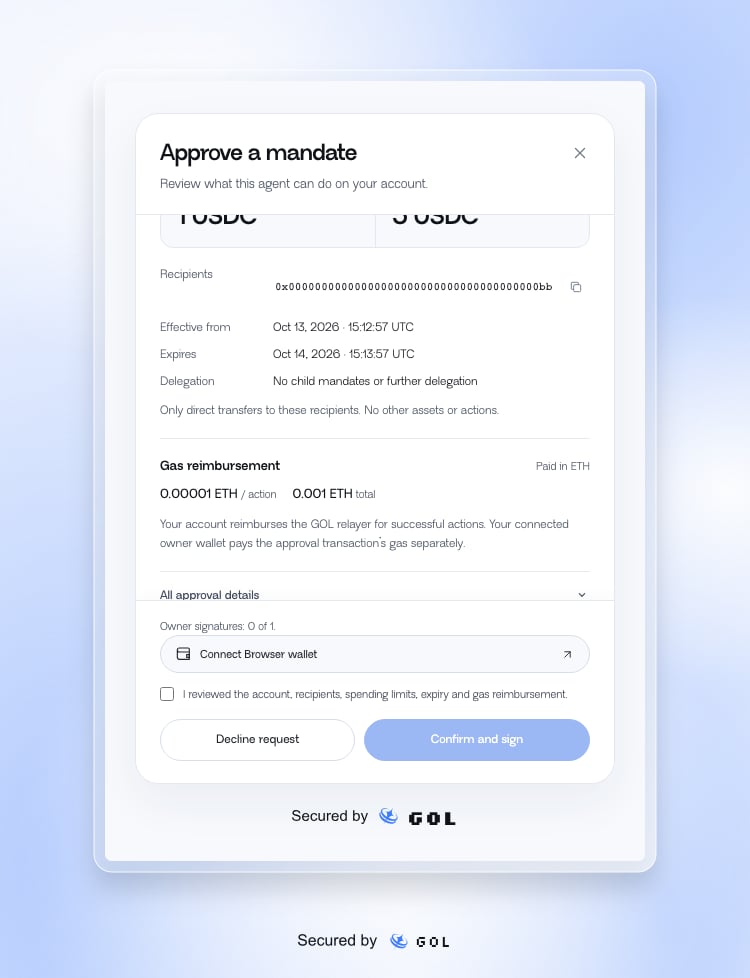
Scroll the terms panel to review expiry, delegation and the exact ETH reimbursement limits before signing.
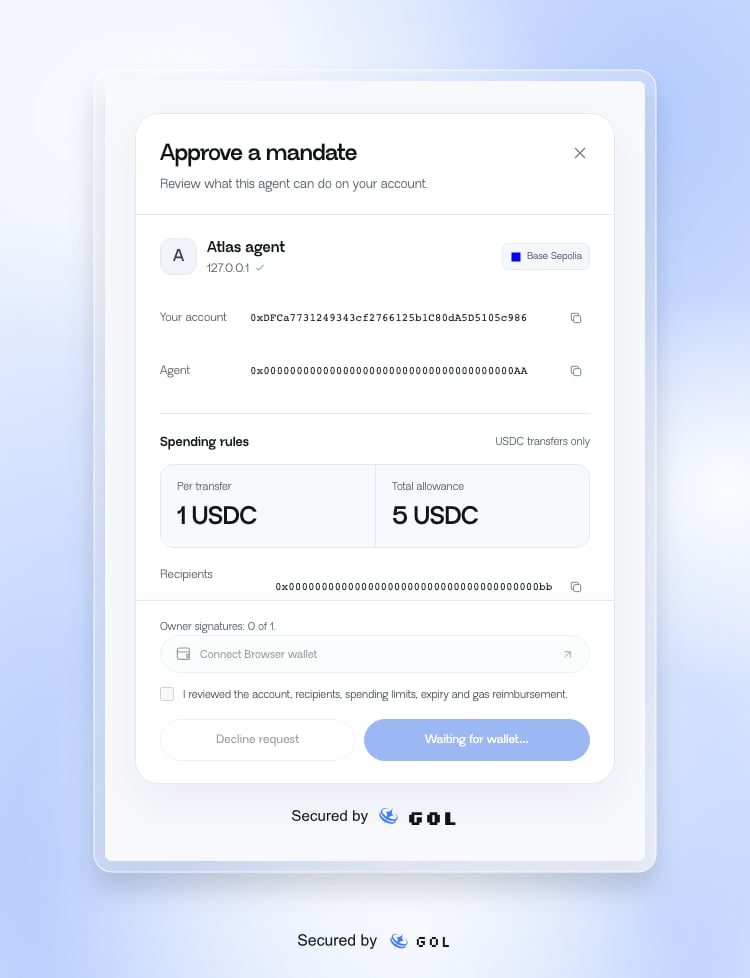
The selected owner wallet must control this exact account. This local capture uses an injected test wallet.
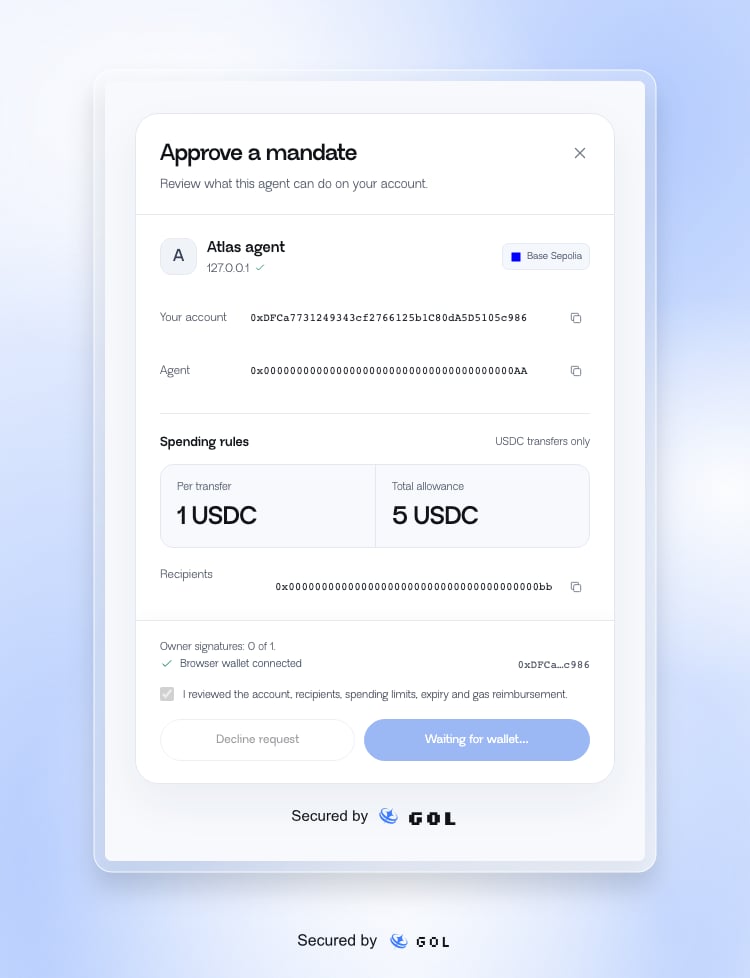
The page waits for the wallet signature after the owner checks the readable terms.
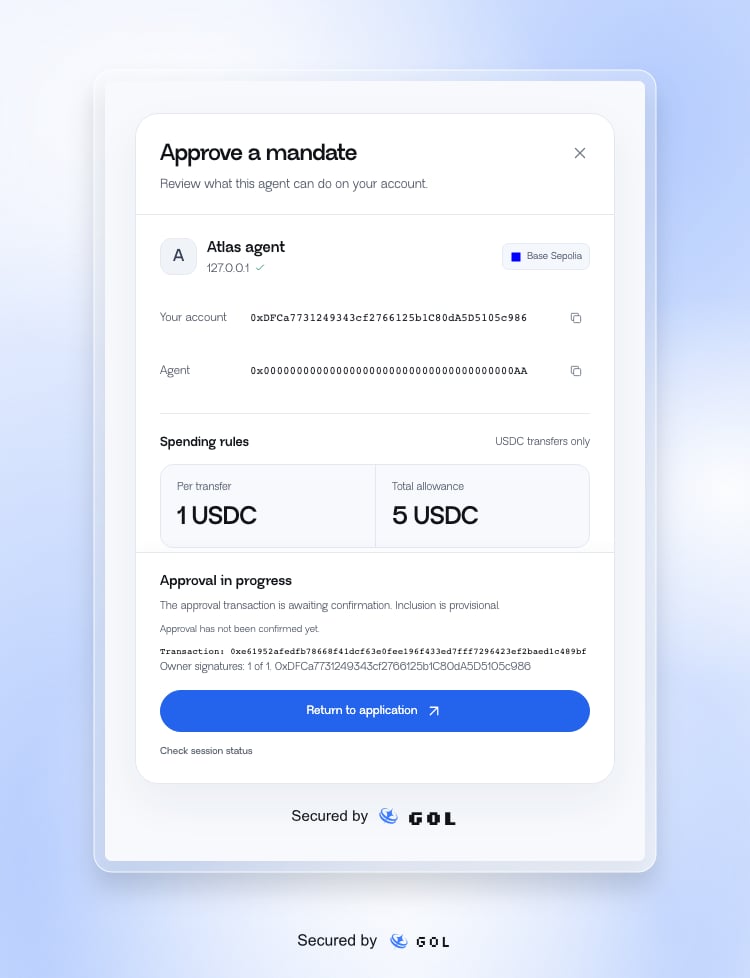
The transaction has been submitted and is awaiting the configured confirmation head. Inclusion remains provisional.
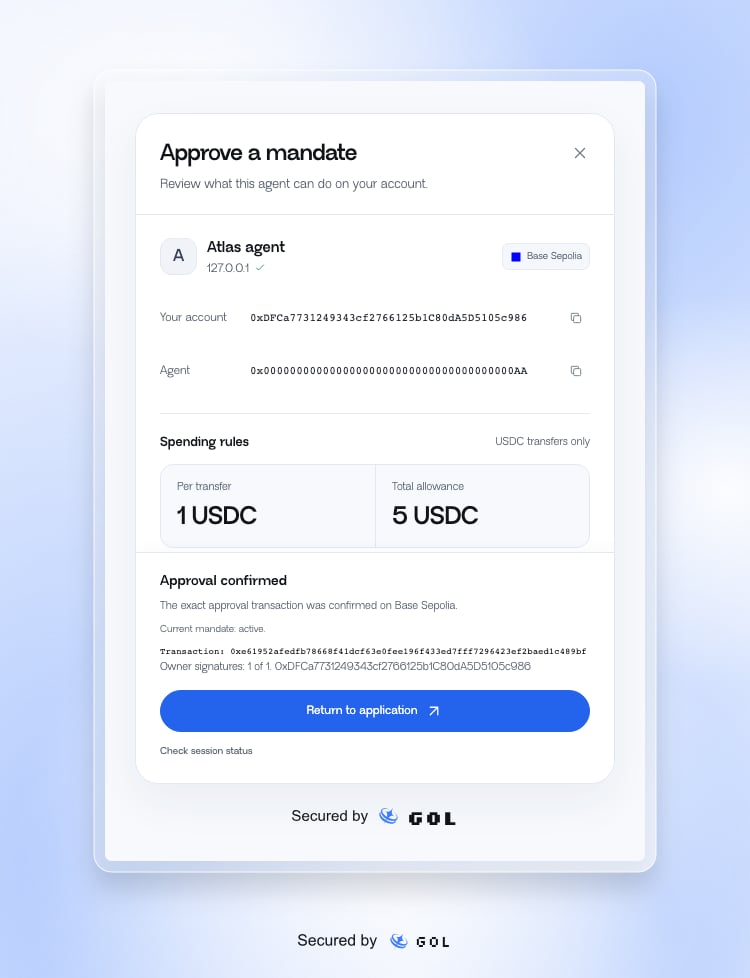
A confirmed result offers the registered return path. The application still re-reads the authoritative API result.
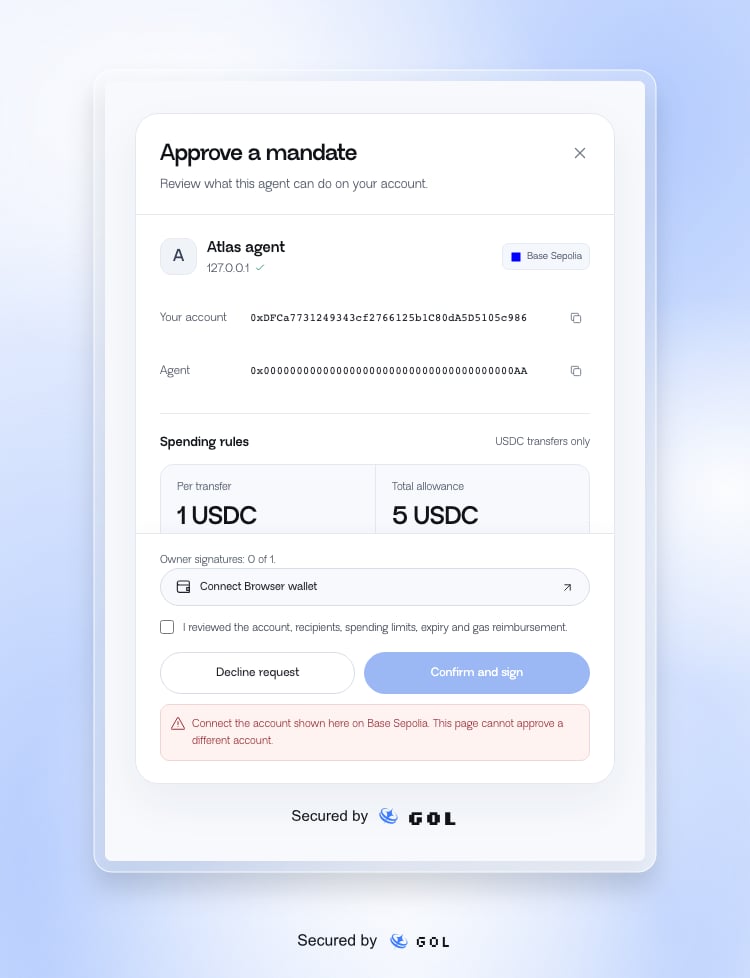
A different wallet cannot approve the account named in the canonical request.
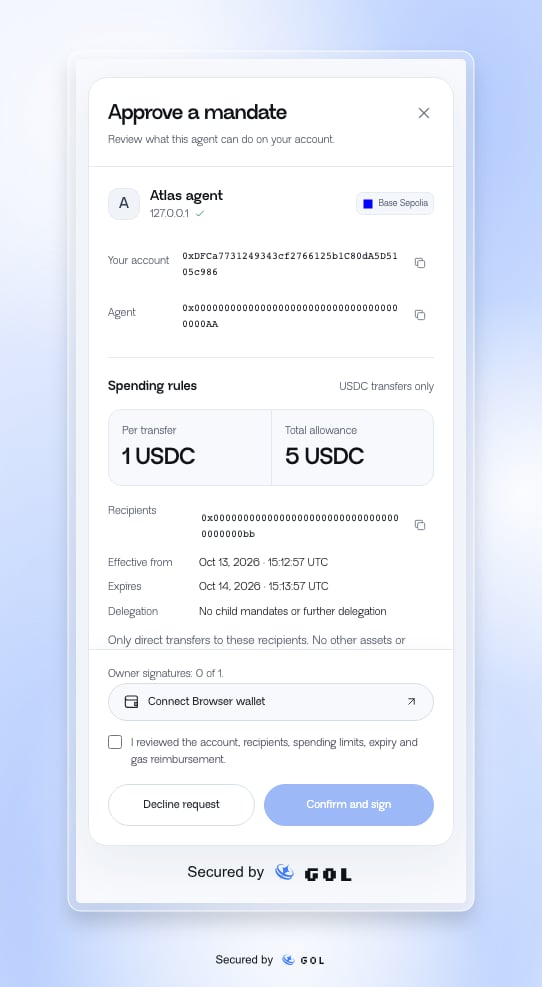
Mobile review uses a full page in a wallet-enabled browser. This capture starts at 390 by 844 pixels.
confirmed requires exact
transaction/events/state at the configured Base confirmation head. Base safe is
not Ethereum finality. Ambiguous sends are indeterminate, never silently retried.
Treat browser messages as hints. Your server must re-read the session through
getApprovalSession(projectId, sessionId), compare it with its saved request,
project and fingerprint, and require confirmed before enabling the agent. A
callback cannot supply replacement authority or an arbitrary return URL.
Owner control and recovery
Setup and approval are separate. An existing EIP-7702 delegation or core installation can remain even when no mandate was approved. Declining an unsigned request creates no mandate through that session. After a wallet signs, GOL cannot retract the signature; its signed deadline or nonce/epoch invalidation bounds its remaining validity. Recover accepted operations through authenticated server lookup and a fresh scoped observation capability. The launch TTL does not stop durable confirmation. Do not ask an owner to sign again just because a popup closed or a transaction hash was lost. Owners can pause/revoke directly through the contract without a page, project key or GOL API. Revocation does not undo transfers or revoke residual token allowances and other account permissions. Those require independent owner actions. Broader family and safety UI coverage requires its own exact configuration and wallet acceptance.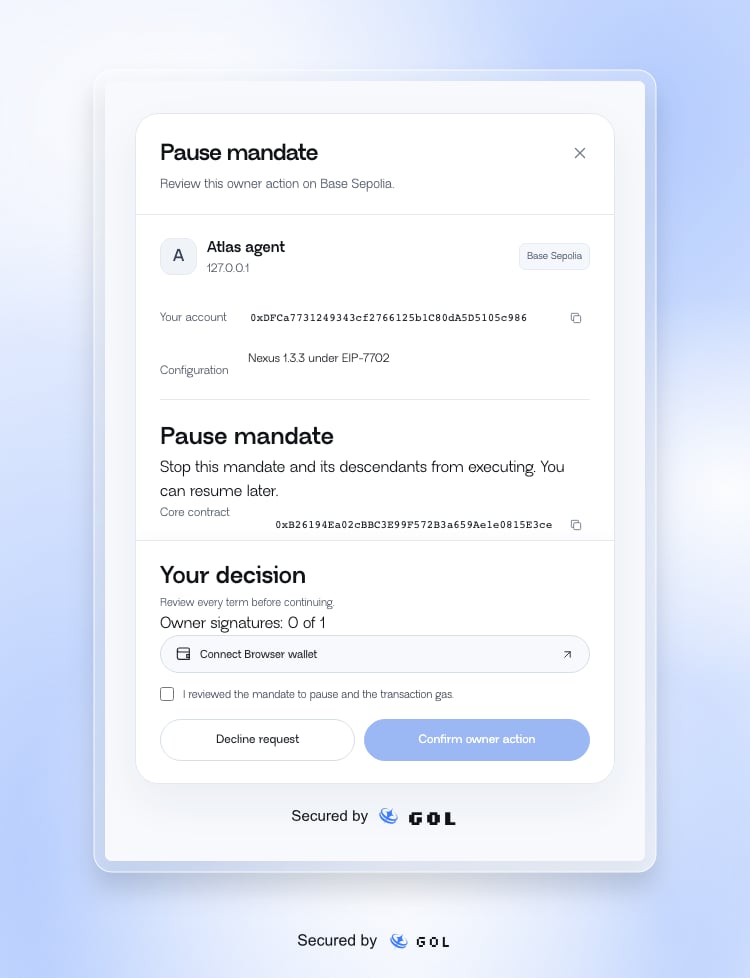
An operation-specific pause request identifies the existing mandate and its effect before asking the owner to sign.